
Aviatrix Clearance limits the reach of compromised cloud and AI workloads
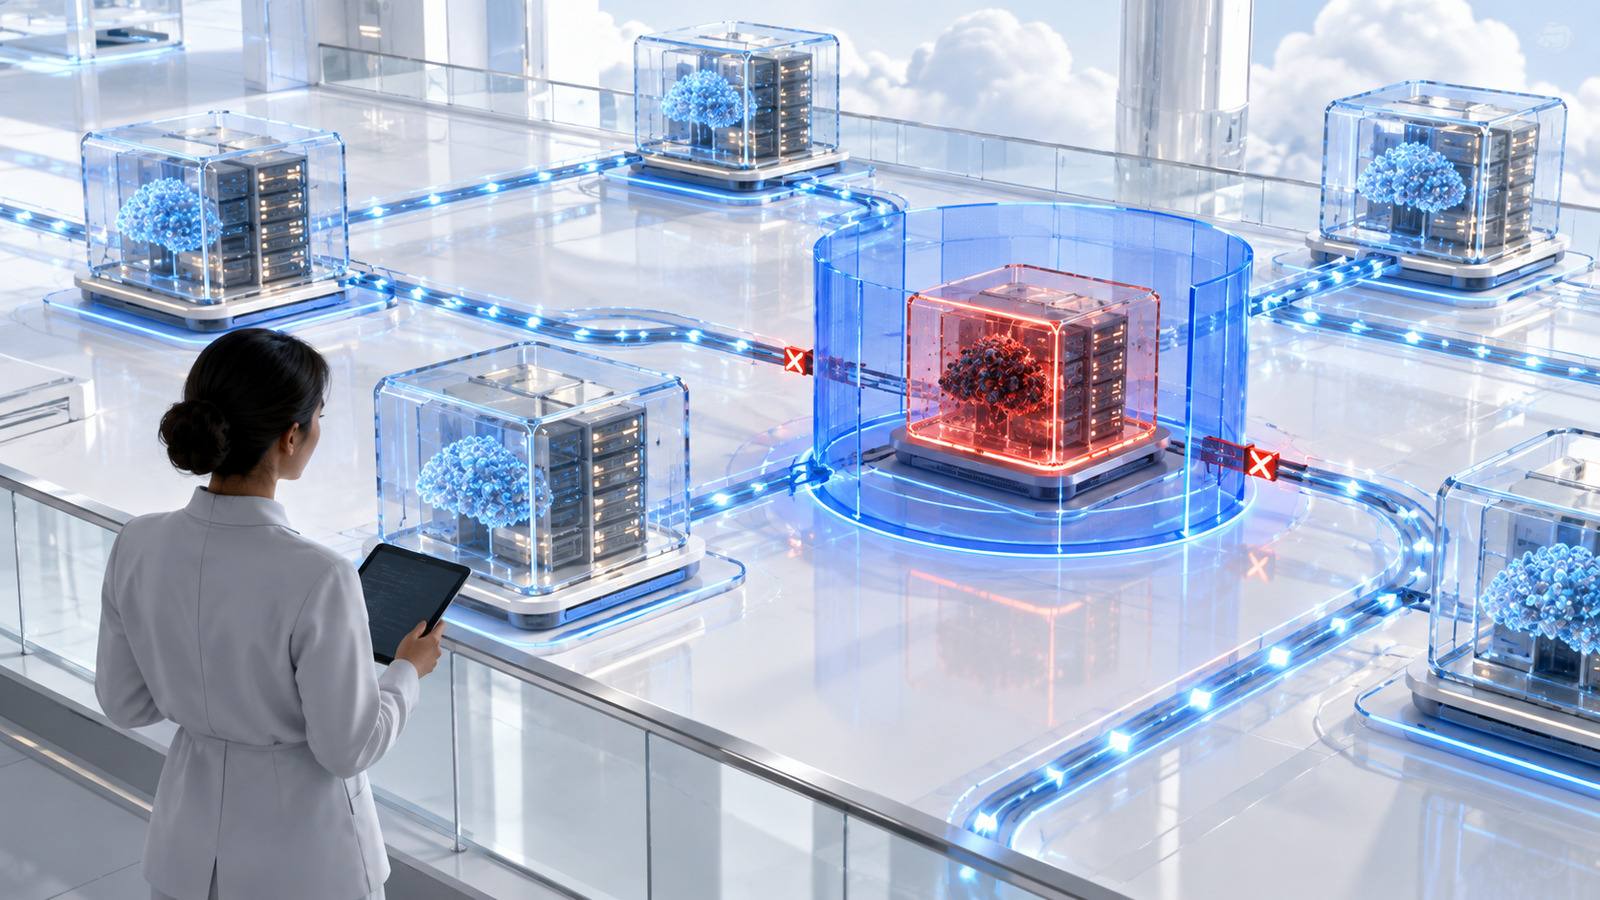
Aviatrix announced Clearance, which restricts cloud workloads to required outbound and lateral connections and lets teams test policies in monitor mode before affecting production traffic.
AT A GLANCE
Key points
- Policies can run in monitor mode before enforcement.
- Clearance covers outbound and lateral workload containment.
- Active Defense is in early access for design partners.
What is changing?
Aviatrix announced Clearance on October 26 as a new offering built on its Containment Platform. The system is designed to limit the external destinations and peer workloads that each workload may reach, using identity and protocol. Before enforcement, a Shadow Rule Set runs alongside live traffic in monitor mode so teams can see which connections would be denied and clear required paths.
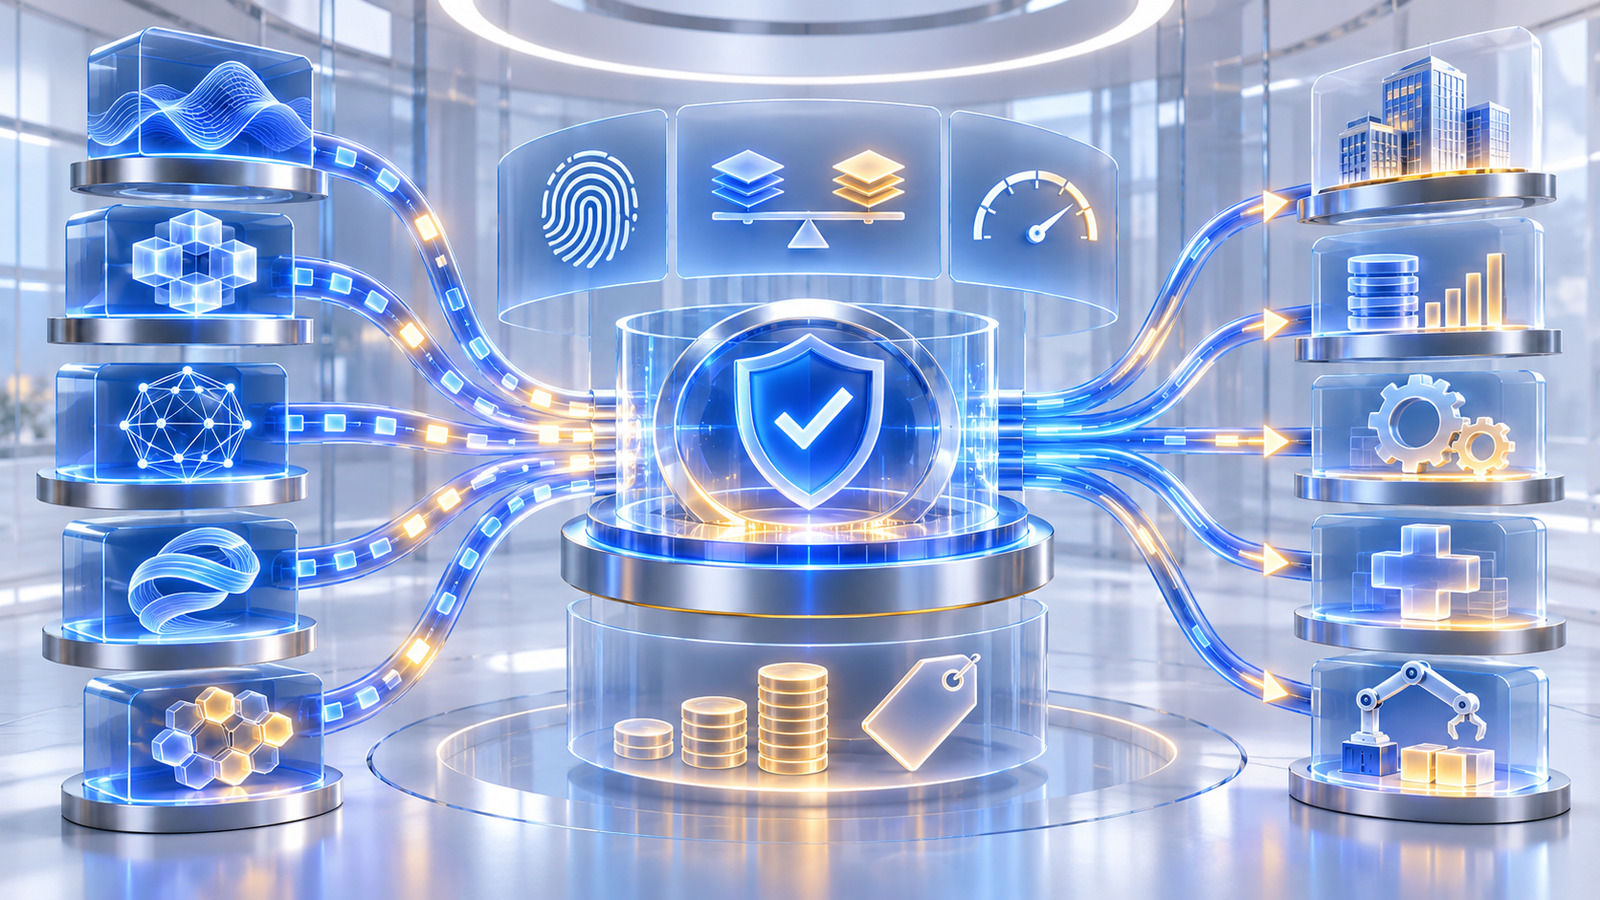
The product consists of Outbound Containment, Lateral Containment, and an Aviatrix Active Defense layer. Aviatrix says Active Defense agents model the environment without a tagging project and draft application policies; that layer is currently in free early access for design partners. Clearance includes an assessment and support for 15 workloads without a time limit. A separate free program for all enterprises runs from November 1, 2026, through May 1, 2027.
Explore the original sources
Source date: 26 October 2026.
Published by AI Radar: 28 Oct 2026, 00:01 (Istanbul, UTC+3). Updated: 28 Oct 2026, 01:12.
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.





Loading comments…