
Brava uses AI agents to test whether defense rules actually work
Brava Security emerged from stealth with $15 million in seed funding; its AI agents exercise attack techniques in a controlled workflow, find SIEM detection gaps and retest the fix.
AT A GLANCE
Key points
- Brava emerged from stealth with $15 million in seed funding.
- AI agents test attack techniques and verify whether the SIEM fires.
- The platform can address a rule or telemetry gap and rerun the test.
What is changing?
Brava Security emerged from stealth on November 4 with $15 million in seed funding. According to Axios and CTech, the round was led by F2 Venture Capital and Pitango. The company says the funding will support product development and commercial expansion in North America.
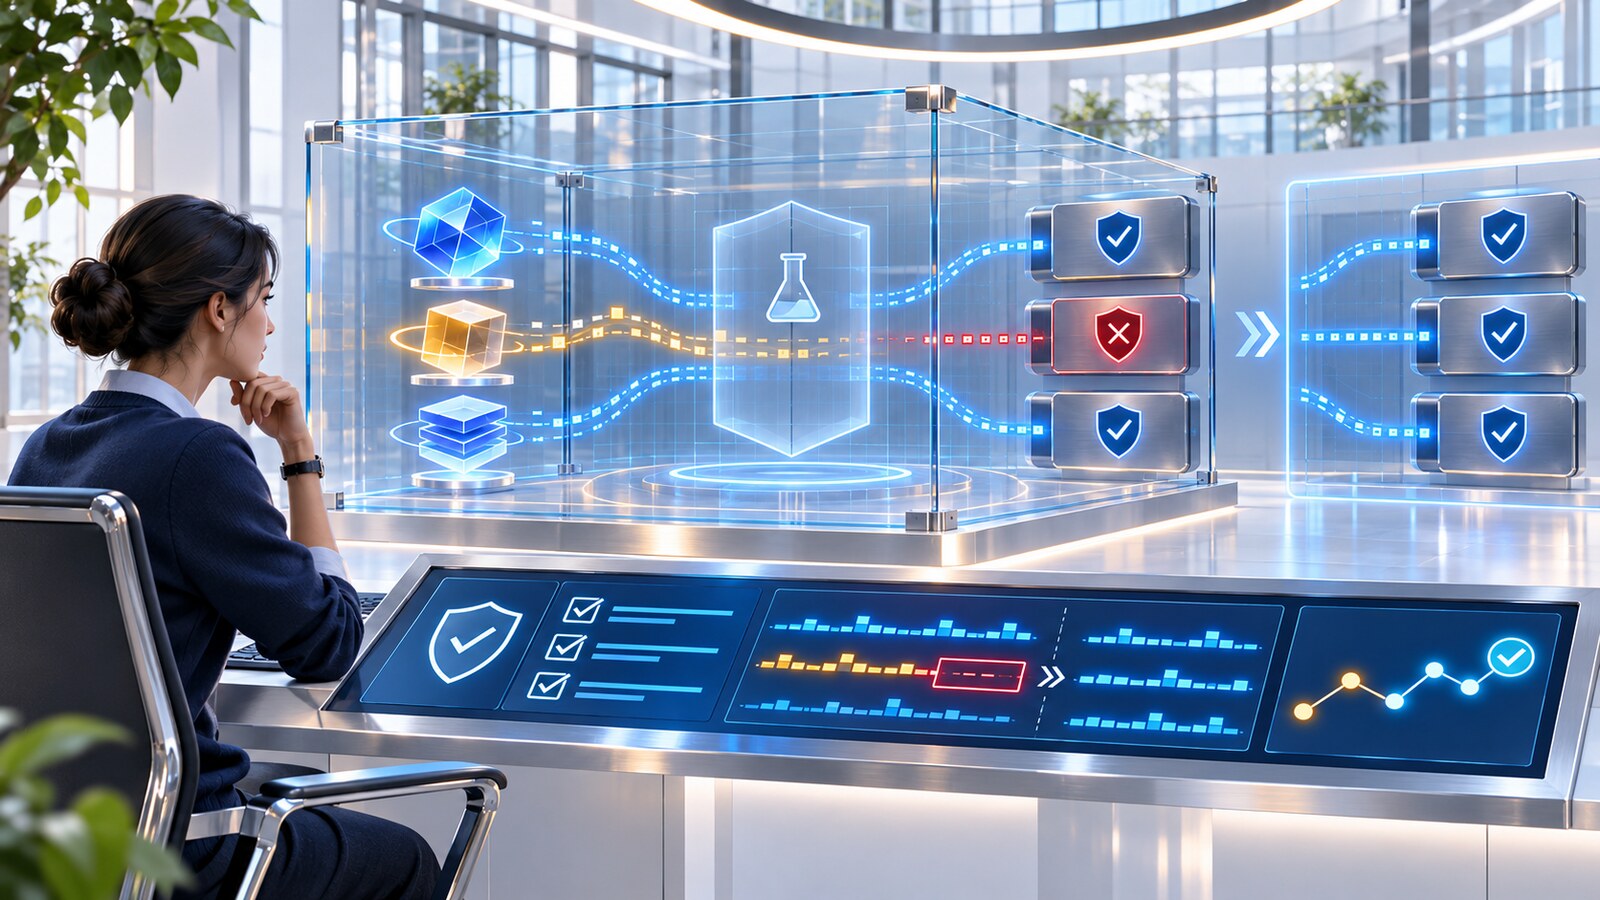
According to Brava’s official product page, AI agents plan the attack path for a defined threat, run techniques in the customer’s environment or a mirror of it, and record the resulting events. The platform then checks whether the SIEM generated an alert, fixes a missing rule or telemetry gap, and runs the test again.
The service also offers natural-language investigation, raw-event evidence and data-pipeline health checks. These are provider claims; teams need to validate test scope, production isolation, permissions and whether every automated change passes through human approval.
Explore the original sources
Source date: 4 November 2026.
Published by AI Radar: 4 Nov 2026, 20:26 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…