
CodeRabbit uses GPT‑6.1 Sol for repository-wide security review
CodeRabbit is using GPT‑6.1 Sol as the primary model in its security agent to inspect changes across files, dependencies, and linked repositories.
AT A GLANCE
Key points
- GPT‑6.1 Sol is the primary model in CodeRabbit’s security agent.
- Deep Scan and CodeRabbit Secure inspect repository and linked-repository context.
- Proposed fixes remain subject to isolated verification and human approval.
What is changing?
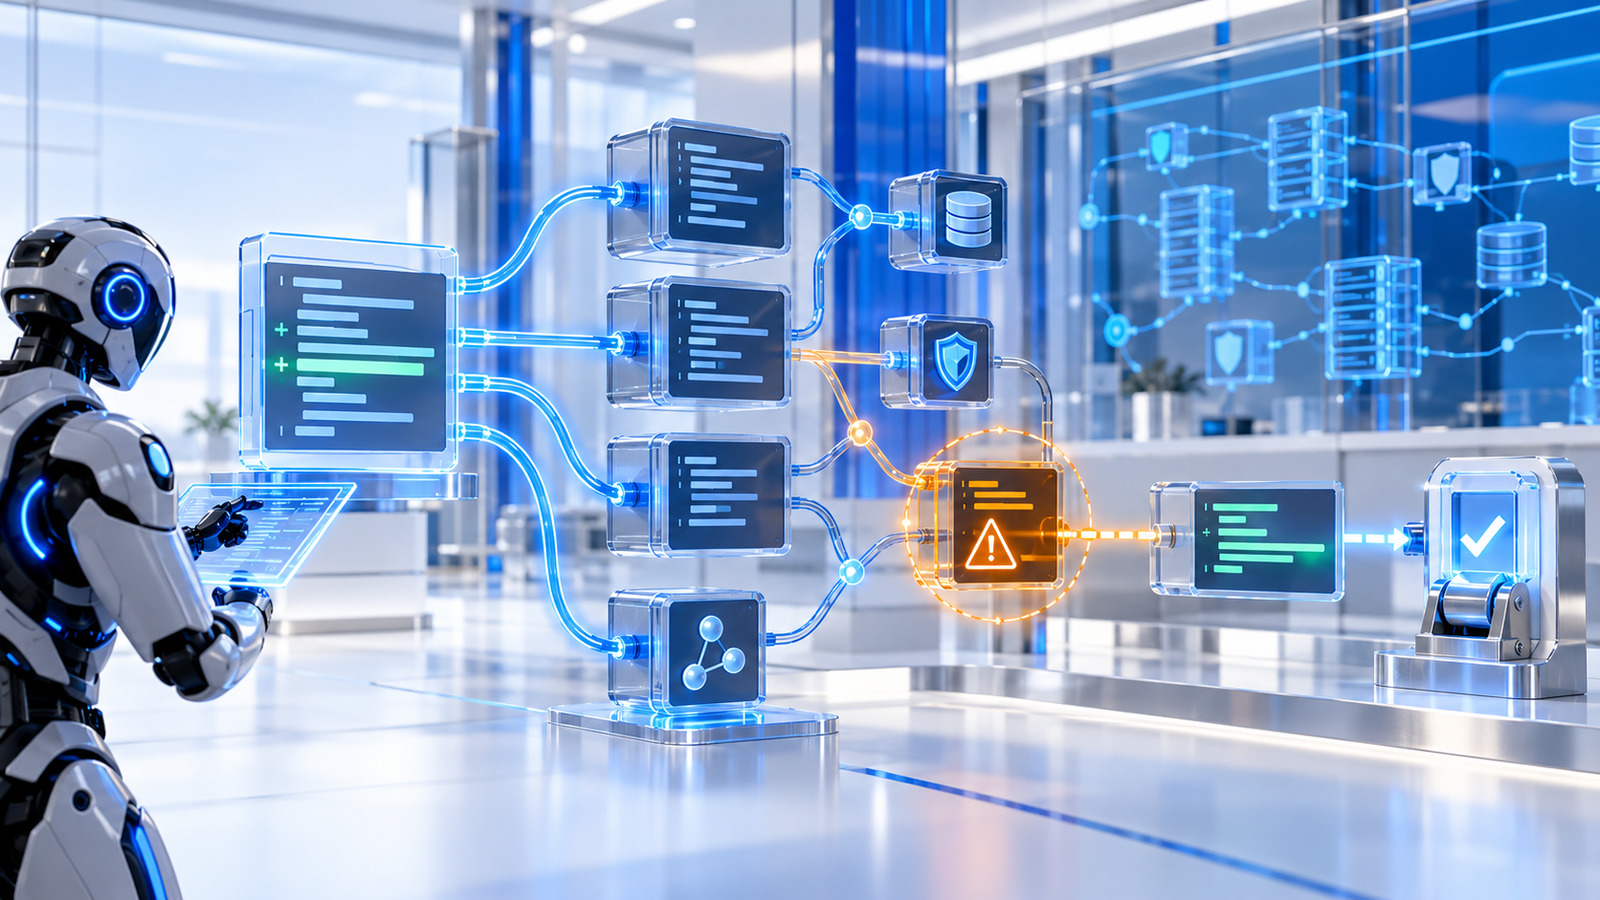
CodeRabbit says it is using GPT‑6.1 Sol as the primary model in its security agent. According to OpenAI, the system evaluates a pull-request change alongside shared libraries, dependencies, and application safeguards rather than reviewing only the modified file. Deep Scan investigates repository-wide interactions, while CodeRabbit Secure can trace impact across linked repositories such as a shared authentication library.
CodeRabbit reports that the model has helped flag security-related issues across thousands of repositories and organizations. User-selected findings can be checked for exploitability in an isolated sandbox without touching production systems. For supported issues, the agent can draft a remediation pull request for a person to review and approve. The review runs independently from the agent that wrote the code and complements established scanners and other security tools.
Explore the original sources
Source date: 26 October 2026.
Published by AI Radar: 27 Oct 2026, 01:08 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…