
IBM makes Agent Identity generally available for governing AI-agent access
IBM Agent Identity is now generally available to register enterprise AI agents in a central inventory and manage delegated authority, short-lived credentials, and audit trails through one control plane.
AT A GLANCE
Key points
- AI agents can be registered in a central inventory with ownership, risk, and tool-connection data.
- OAuth-based short-lived, task-scoped tokens are supported.
- IBM Verify, HashiCorp Vault, and watsonx Orchestrate connect identity, credentials, and auditability.
What is changing?
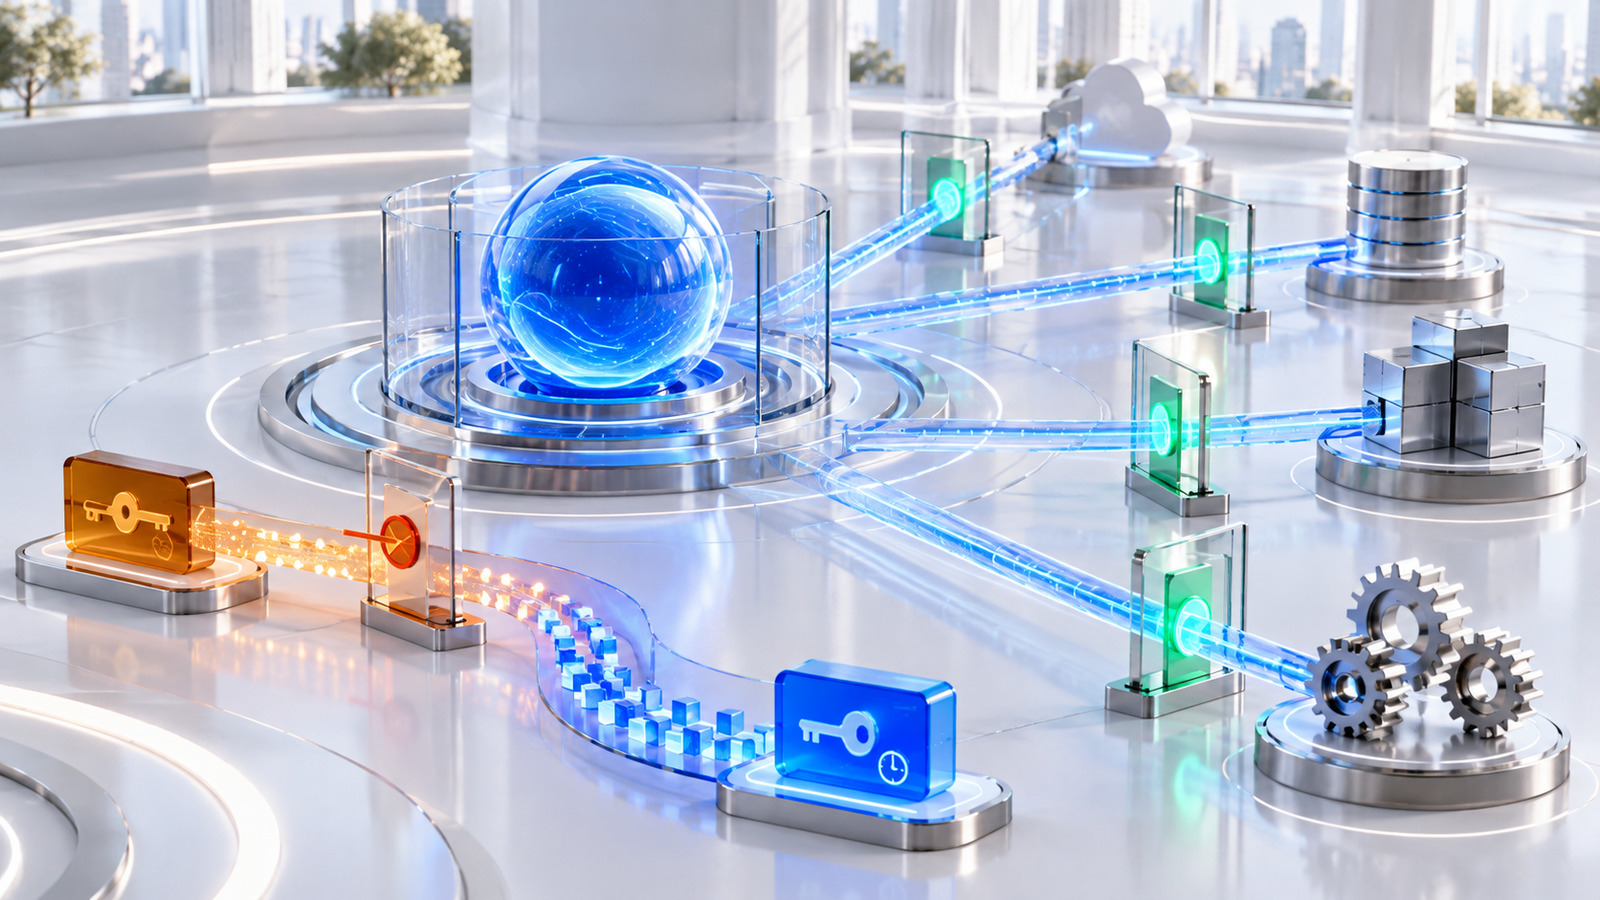
IBM made Agent Identity generally available on October 26. The system registers AI agents as first-class identities in a central inventory, bringing ownership and risk metadata, approved tool connections, and lifecycle state together. This gives organizations a consistent way to see which agents are operating, who owns them, and what authority they are using.
The product preserves on-behalf-of delegation across identity providers and token exchanges. It supports OAuth-based short-lived, task-scoped tokens, contextual authorization, runtime risk evaluation, and structured audit trails. IBM Verify provides the identity and policy layer, while HashiCorp Vault protects target-specific credentials issued when needed instead of relying on long-lived secrets. Agents managed through watsonx Orchestrate can also enter the same governance path.
Explore the original sources
Source date: 26 October 2026.
Published by AI Radar: 27 Oct 2026, 08:01 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…