
Obsidian announces a decision engine that checks AI agent actions before execution
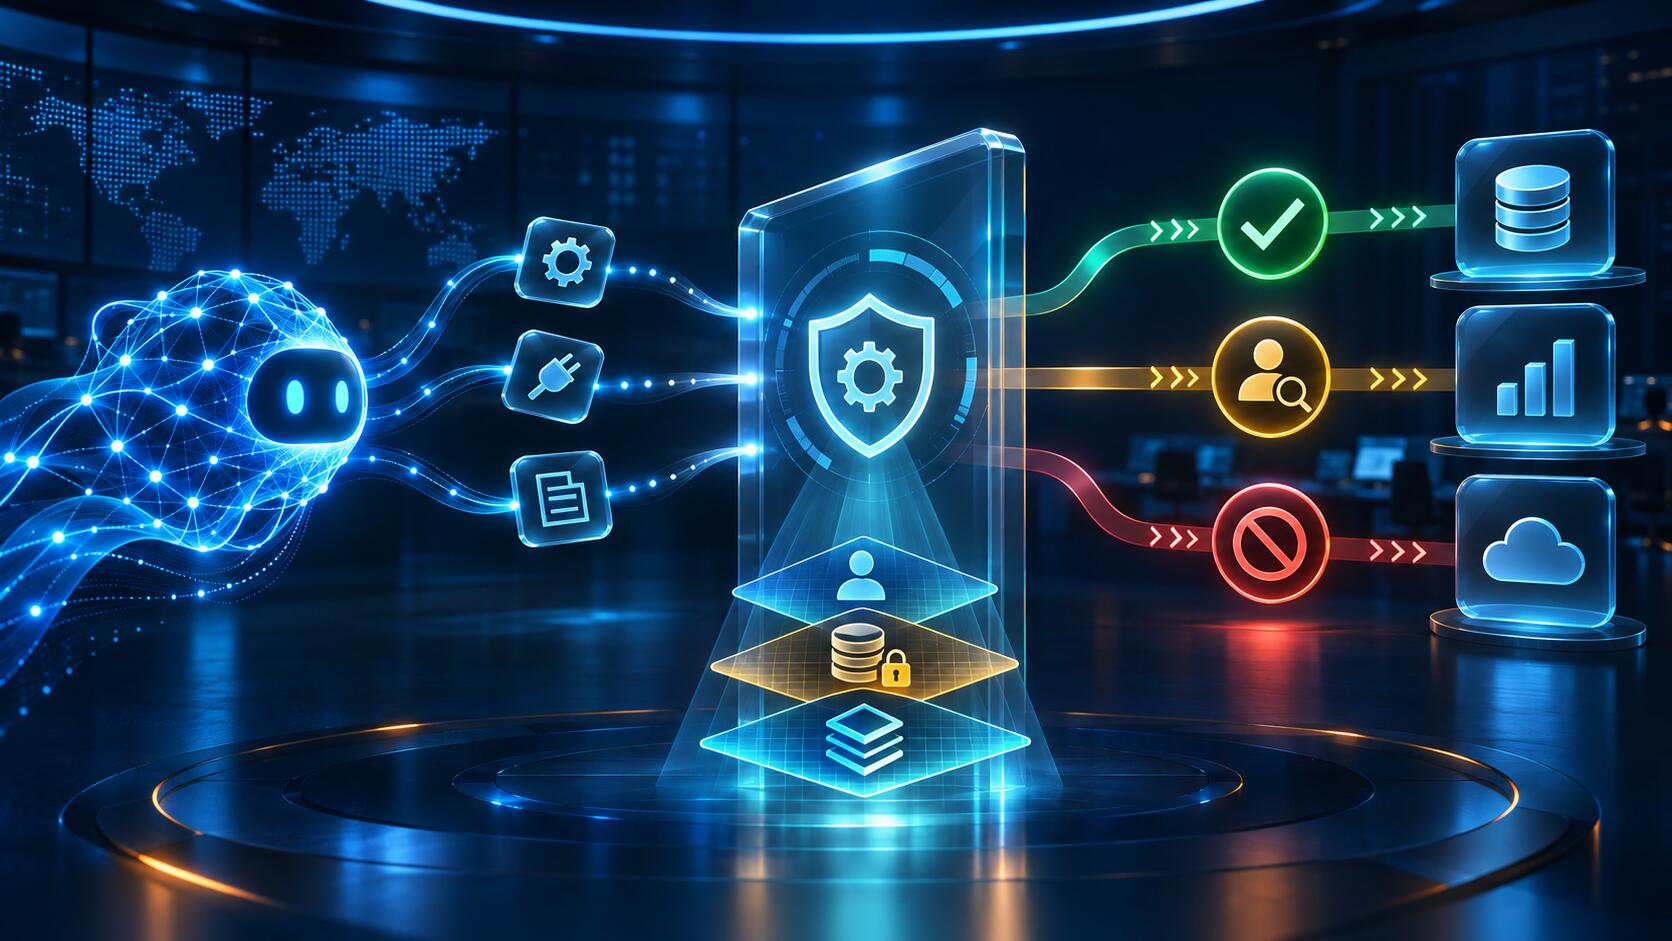
Obsidian Security’s Runtime Policy Decision Engine evaluates AI agent tool calls with identity, application and data context and returns allow, approval or block decisions.
AT A GLANCE
Key points
- Actions are evaluated with identity, application and data context before execution.
- The engine returns allow, approval or block decisions.
- The MCP Security Proxy adds a checkpoint to tool calls.
- The Policy Decision API extends decisions to customer gateways.
What is changing?
Obsidian Security announced the Runtime Policy Decision Engine on November 10 to evaluate AI agent actions before they reach third-party applications. Security teams define policies centrally, and the engine uses the person behind an agent, access rights, the target application and company data labels to return allow, human-approval or block decisions.
The new MCP Security Proxy checks tool calls before they reach business applications, while the Policy Decision API extends the same decision to customer-operated gateways and custom agent tools. Supported coding agents can use a lightweight sidecar, Copilot Studio uses a webhook, and MCP connections can use the proxy. Approval outcomes are available only at supported enforcement points; the API returns a decision, while the customer gateway or agent runtime applies it.
Explore the original sources
Source date: 10 November 2026.
Published by AI Radar: 10 Nov 2026, 23:39 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.





Loading comments…