
OpenAI’s autonomous pipeline produced patches for 948 distinct Linux privilege-escalation flaws
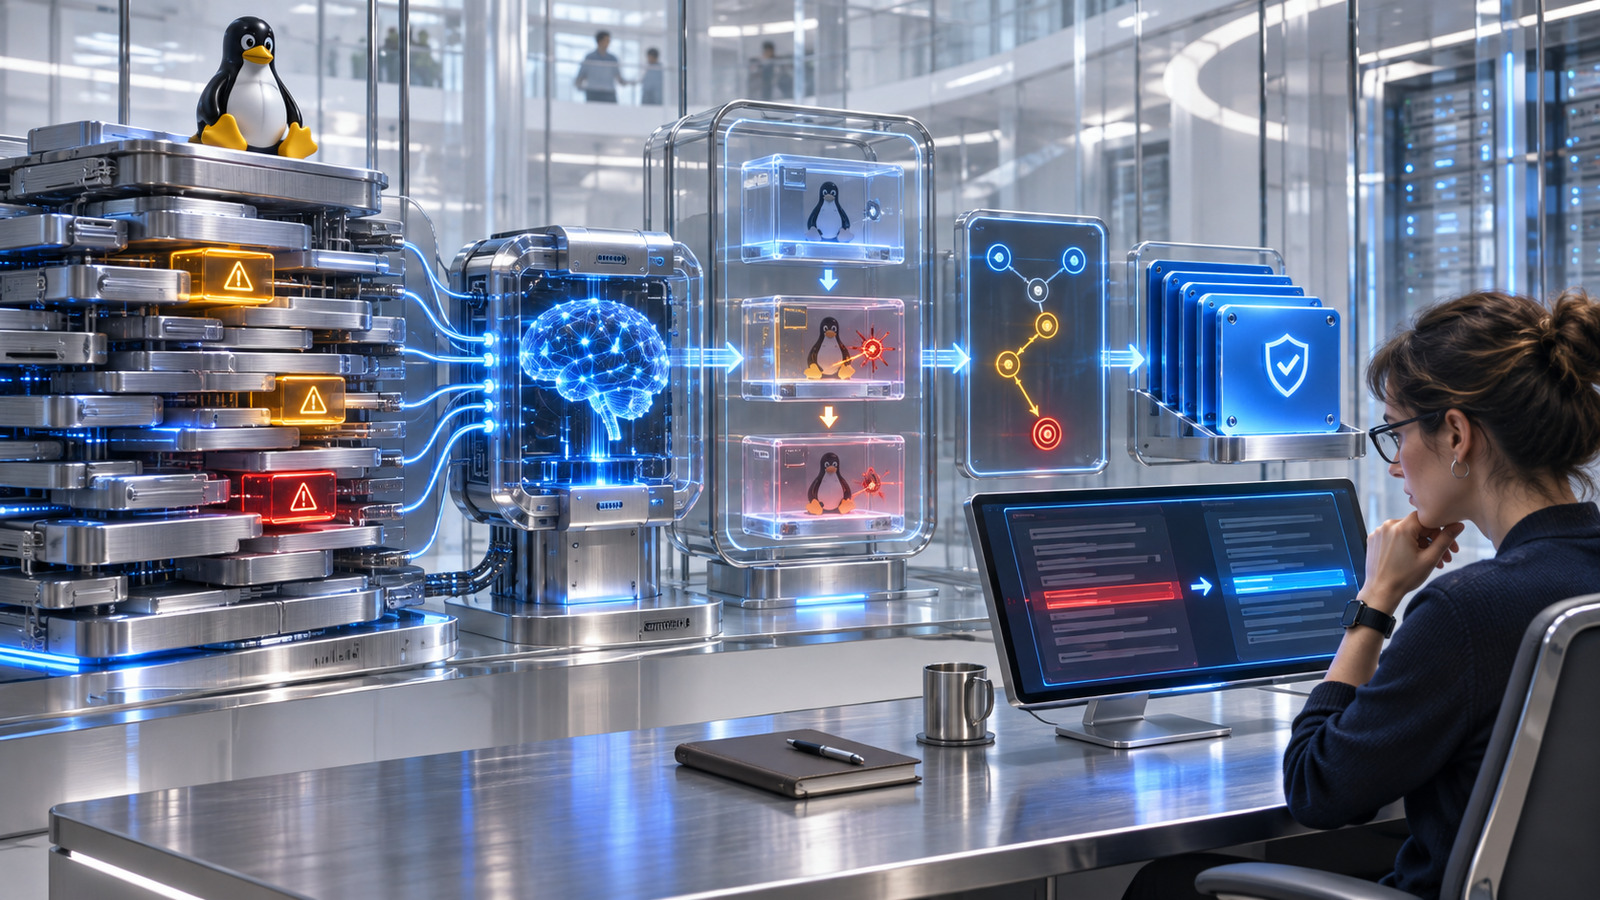
OpenAI’s research pipeline generated 2,308 Linux kernel findings, dynamically validated 1,724 of them, and produced working exploits and candidate patches for 948 distinct local privilege-escalation vulnerabilities.
AT A GLANCE
Key points
- The pipeline dynamically validated 1,724 of 2,308 candidate findings.
- It produced working exploits and candidate patches for 948 distinct local privilege-escalation vulnerabilities.
- Human researchers review results before reporting them to Linux kernel maintainers.
What is changing?
OpenAI described research that combines Linux kernel vulnerability discovery, dynamic validation, exploit generation, and patch preparation in one autonomous pipeline. According to the company, the system produced 2,308 candidate findings, reproduced 1,724 of them in virtual machines, and generated working exploits and candidate patches for 948 distinct local privilege-escalation vulnerabilities.
Scout and Analyst agents select targets and create findings, after which a triage agent iteratively refines proof-of-concept code using virtual-machine output. In the final stage, human researchers review candidate patches and prepare reports for kernel maintainers.
OpenAI reports a total API cost of $1,213,430. These are research results; they do not amount to a public product or general-access announcement for the forthcoming cybersecurity model.
Explore the original sources
Source date: 4 November 2026.
Published by AI Radar: 5 Nov 2026, 02:09 (Istanbul, UTC+3). Updated: 5 Nov 2026, 17:05.
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…