
CodeRabbit rebuilds software delivery around Codex agents
According to an OpenAI case study, CodeRabbit embedded Codex across incident triage and security workflows; the company reports shipping roughly 20 times more software with the same team over six months.
AT A GLANCE
Key points
- Codex turns incident and support triage into review-ready pull requests.
- The reported 20x delivery increase is CodeRabbit's own claim.
- Low-risk changes can auto-ship while others retain human approval.
What is changing?
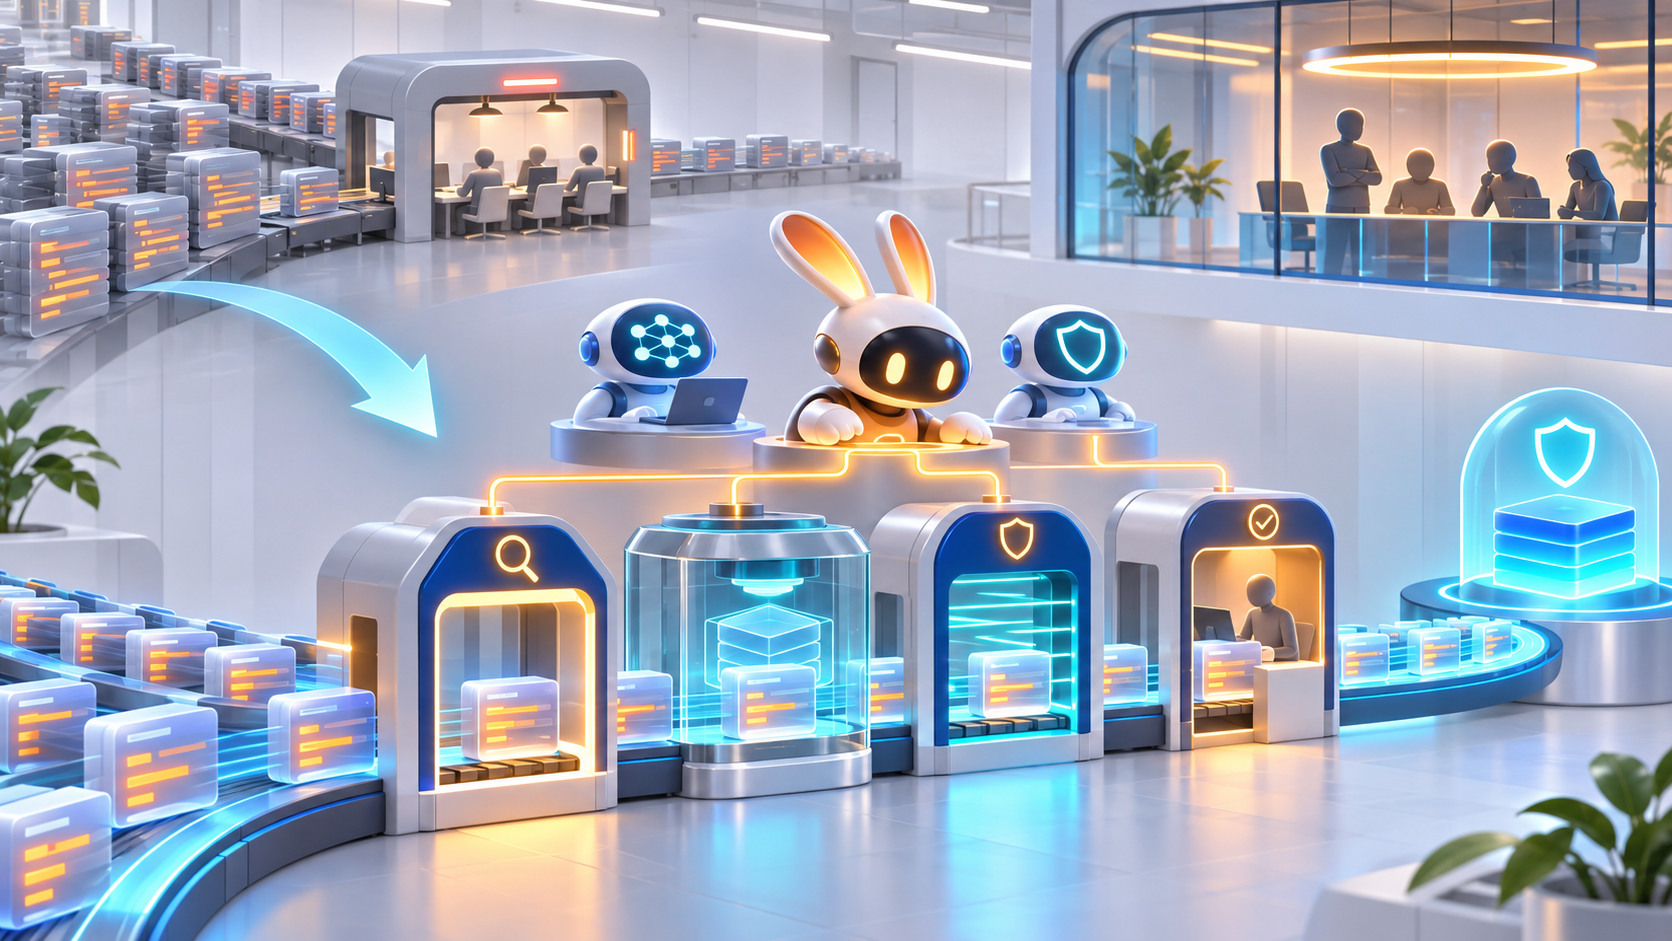
CodeRabbit said in a case study published with OpenAI that it has embedded Codex into code review, incident triage and security workflows. Its Slack bot classifies incidents, messages and support tickets, then prepares a pull request for engineers to review. Running multiple agents in parallel required the company to redesign its release process and human approval points.
CodeRabbit says it shipped roughly 20 times more software over the past six months without increasing engineering headcount. It also reports that a CodeRabbit Secure promotion built with Daybreak and Codex found 43,000 vulnerabilities across 13,000 scans. These figures are provider-reported case-study results, not an independent benchmark.
Explore the original sources
Source date: 9 November 2026.
Published by AI Radar: 10 Nov 2026, 02:12 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.






Loading comments…