
NVIDIA OpenShell adds a hardware-backed security layer for AI agents
The OpenShell Reference Architecture combines running, observing, containing and enforcing policies on enterprise AI agents in one infrastructure design.
AT A GLANCE
Key points
- Combines agent creation, isolation, observation and policy enforcement in one architecture.
- Brings together Vera Rubin, Vera CPUs, the OpenShell runtime and BlueField‑4.
- Lists support for Linux, Kubernetes and Windows Execution Containers.
- Available now, but production behavior and performance impact still require environment-specific validation.
What is changing?
NVIDIA announced the OpenShell Reference Architecture on October 21. The company introduced a full-stack reference design for building, isolating, observing and governing AI agents running across enterprise and edge systems. The architecture is available now.
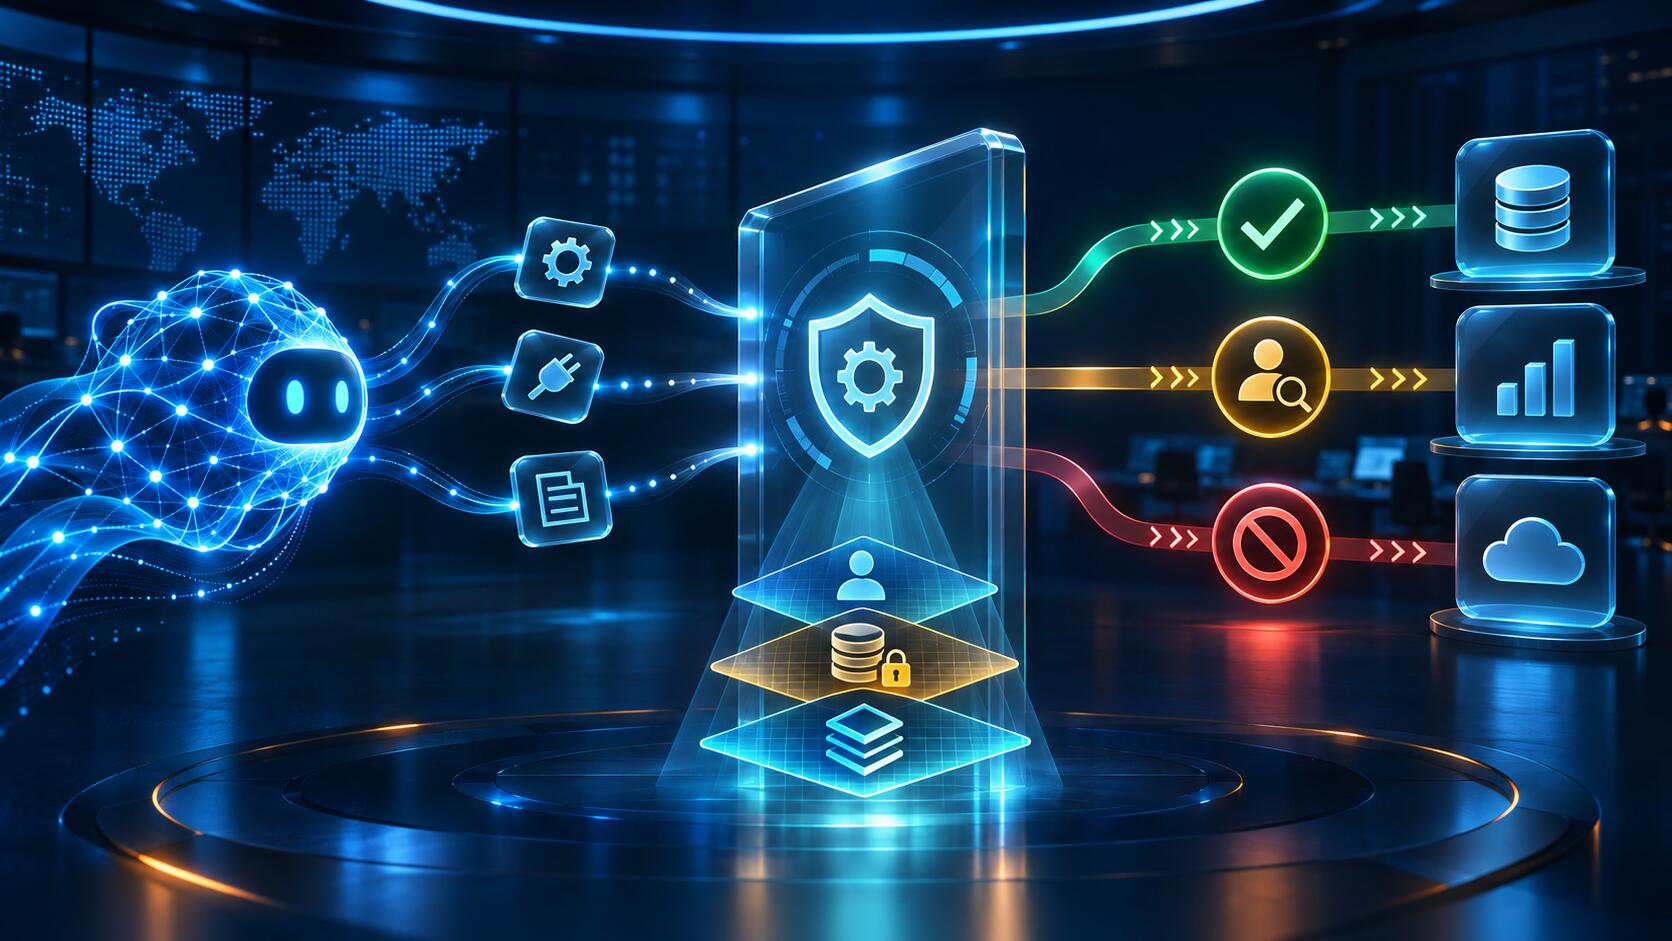
The design combines Vera Rubin systems for model inference, Vera CPUs for agent harnesses and tool use, the open-source OpenShell secure runtime, and BlueField‑4 DPUs that monitor behavior at the hardware layer. NVIDIA Sentry is intended to quarantine and stop an agent that attempts to move outside its software boundary.
OpenShell can run on Linux and Kubernetes infrastructure as well as Microsoft Windows Execution Containers. NVIDIA says a broad group of cloud, security and enterprise-software partners are developing integrations. These are company statements about partner work; independent production results have not yet been published.
Explore the original sources
Source date: 21 October 2026.
Published by AI Radar: 21 Oct 2026, 15:08 (Istanbul, UTC+3). Updated: 21 Oct 2026, 16:02.
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…