
Cogent uses OpenAI models to move enterprise vulnerabilities toward verified remediation
Cogent Security combines OpenAI models with enterprise context and policy controls to manage vulnerabilities from investigation through verified remediation.
AT A GLANCE
Key points
- Enterprise context supports investigation through verified remediation
- Deterministic policies and a separate gateway constrain agent actions
- Reported customer gains require independent validation
What is changing?
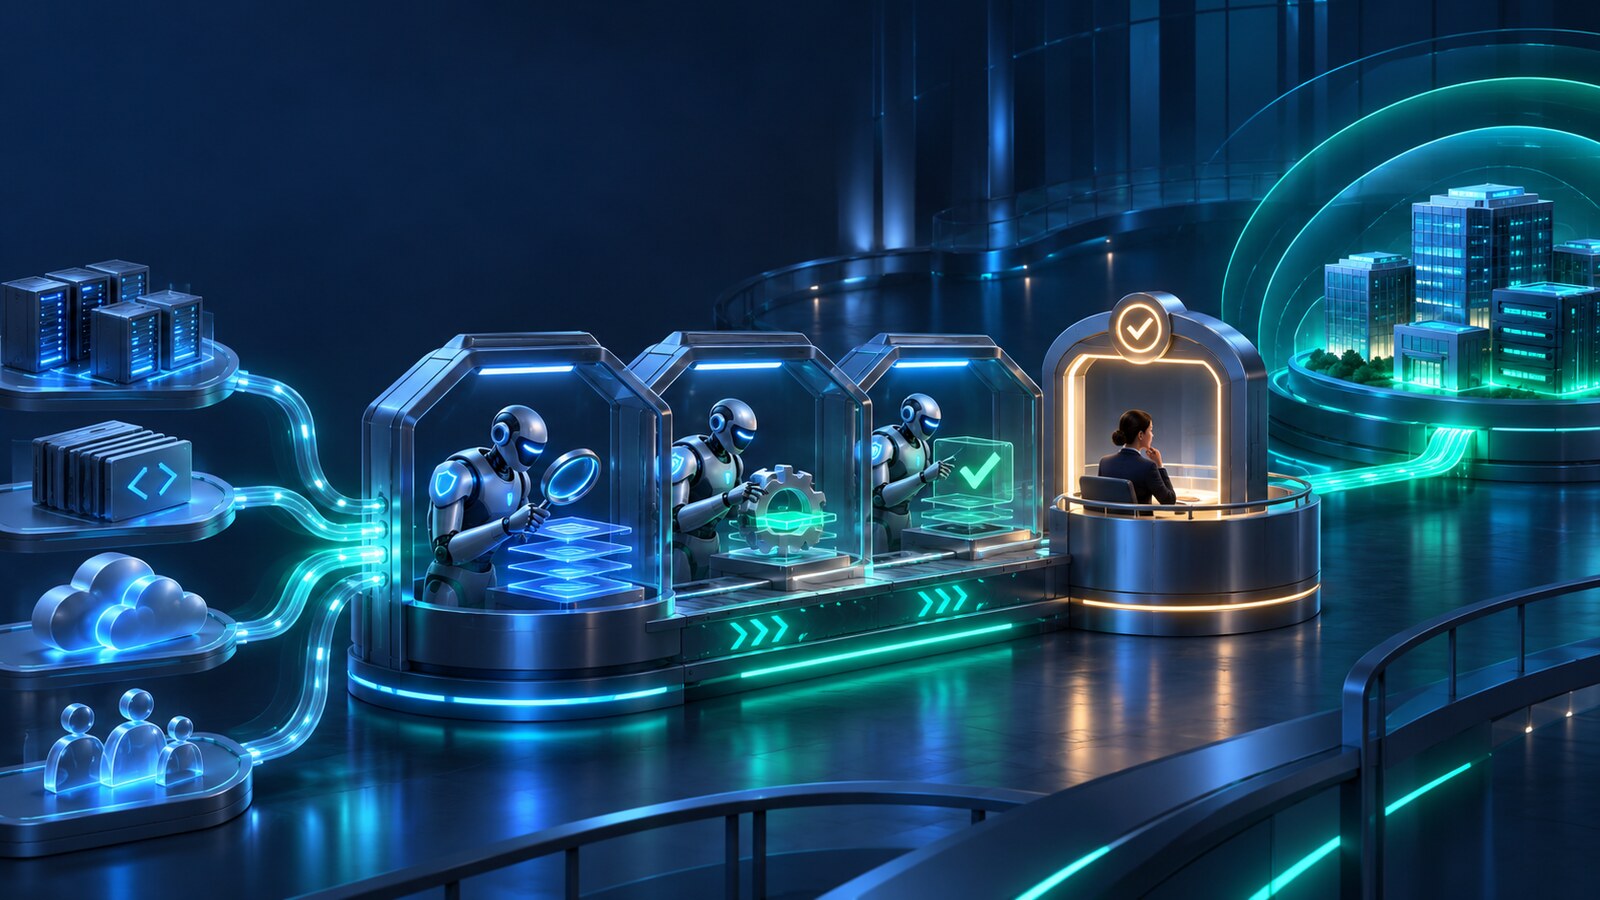
According to OpenAI’s November 10 customer story, Cogent Security’s Cyber Defense Factories combine asset, identity, ownership, and dependency data in a shared context layer. Agents investigate vulnerabilities, execute permitted changes, and verify that the risk has been removed.
GPT‑6 Astra handles planning and complex reasoning, GPT‑6.1 Sol supports general execution, and GPT‑5.6 is used for more routine vulnerability-management work. A policy engine called TRACE checks tool calls against deterministic rules, while a separate gateway verifies authorization and higher-risk work can run in isolated environments.
Cogent reports a 75% reduction in mean time to remediate critical vulnerabilities for an automotive customer and a fivefold increase in triage capacity for an IT-services customer. These are company- and customer-reported results and require independent validation across different environments.
Explore the original sources
Source date: 10 November 2026.
Published by AI Radar: 11 Nov 2026, 09:08 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.






Loading comments…