
Sysdig AI Defense governs agent actions at runtime from endpoint to cloud
Sysdig made AI Defense generally available, comparing an AI agent’s stated intent with its actual operating-system-level actions.
AT A GLANCE
Key points
- Agent intent and kernel-observed operations are evaluated together.
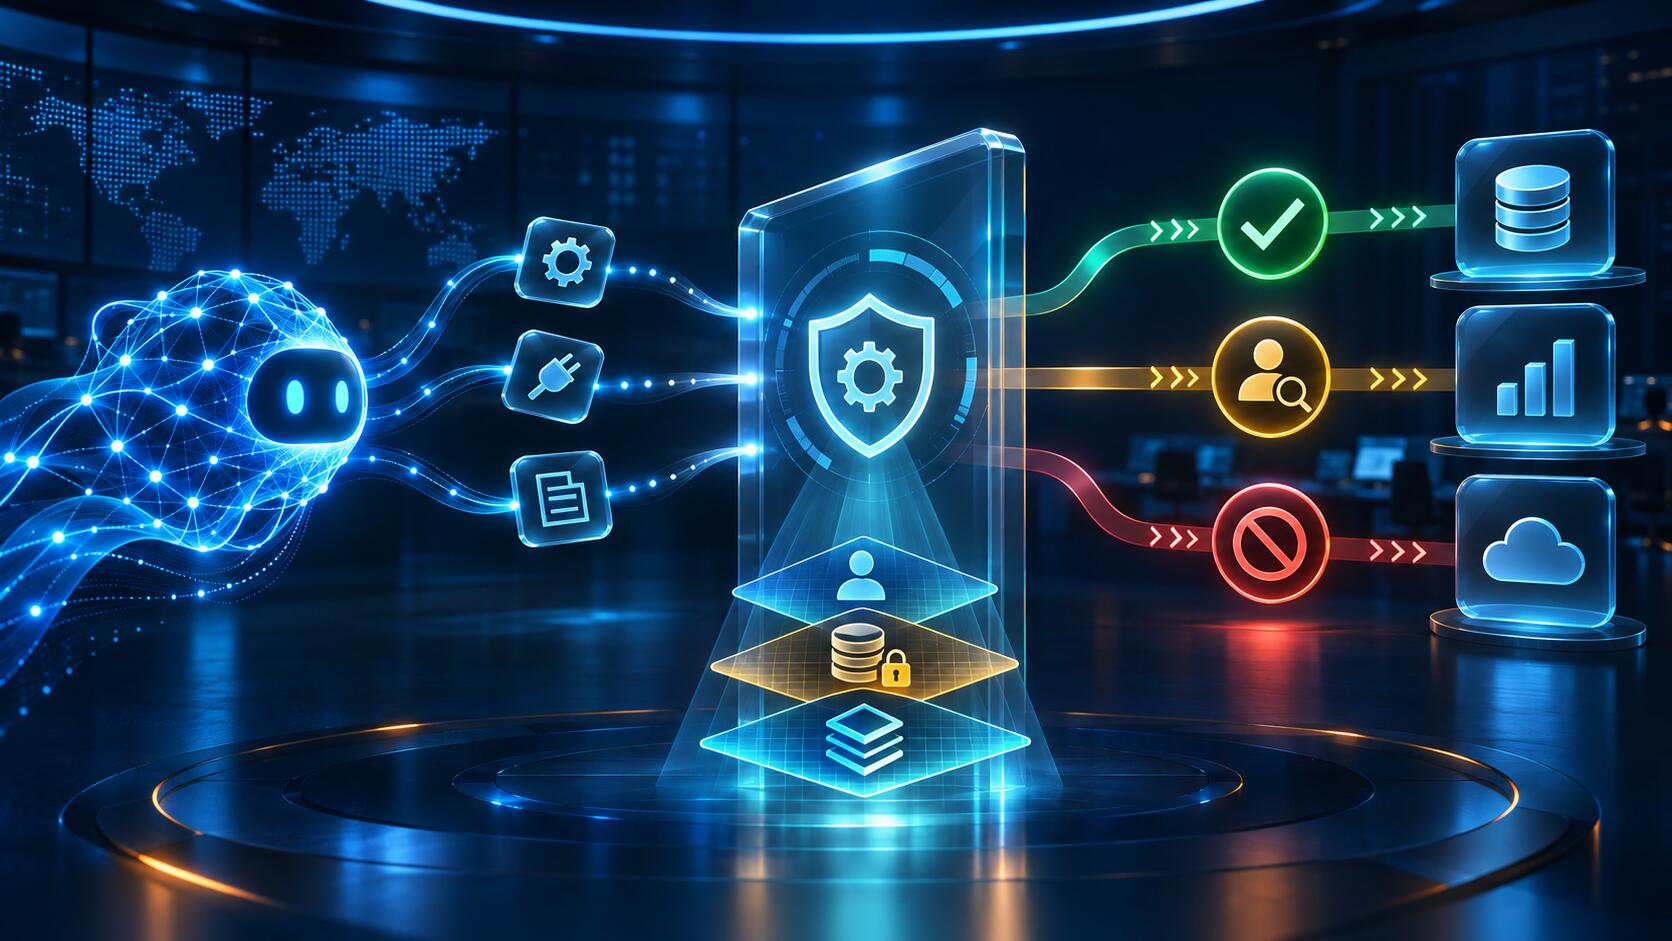
- Policy can route each action to allow, confirmation or block.
- Endpoint activity is linked with cloud resources reachable by the same identity.
What is changing?
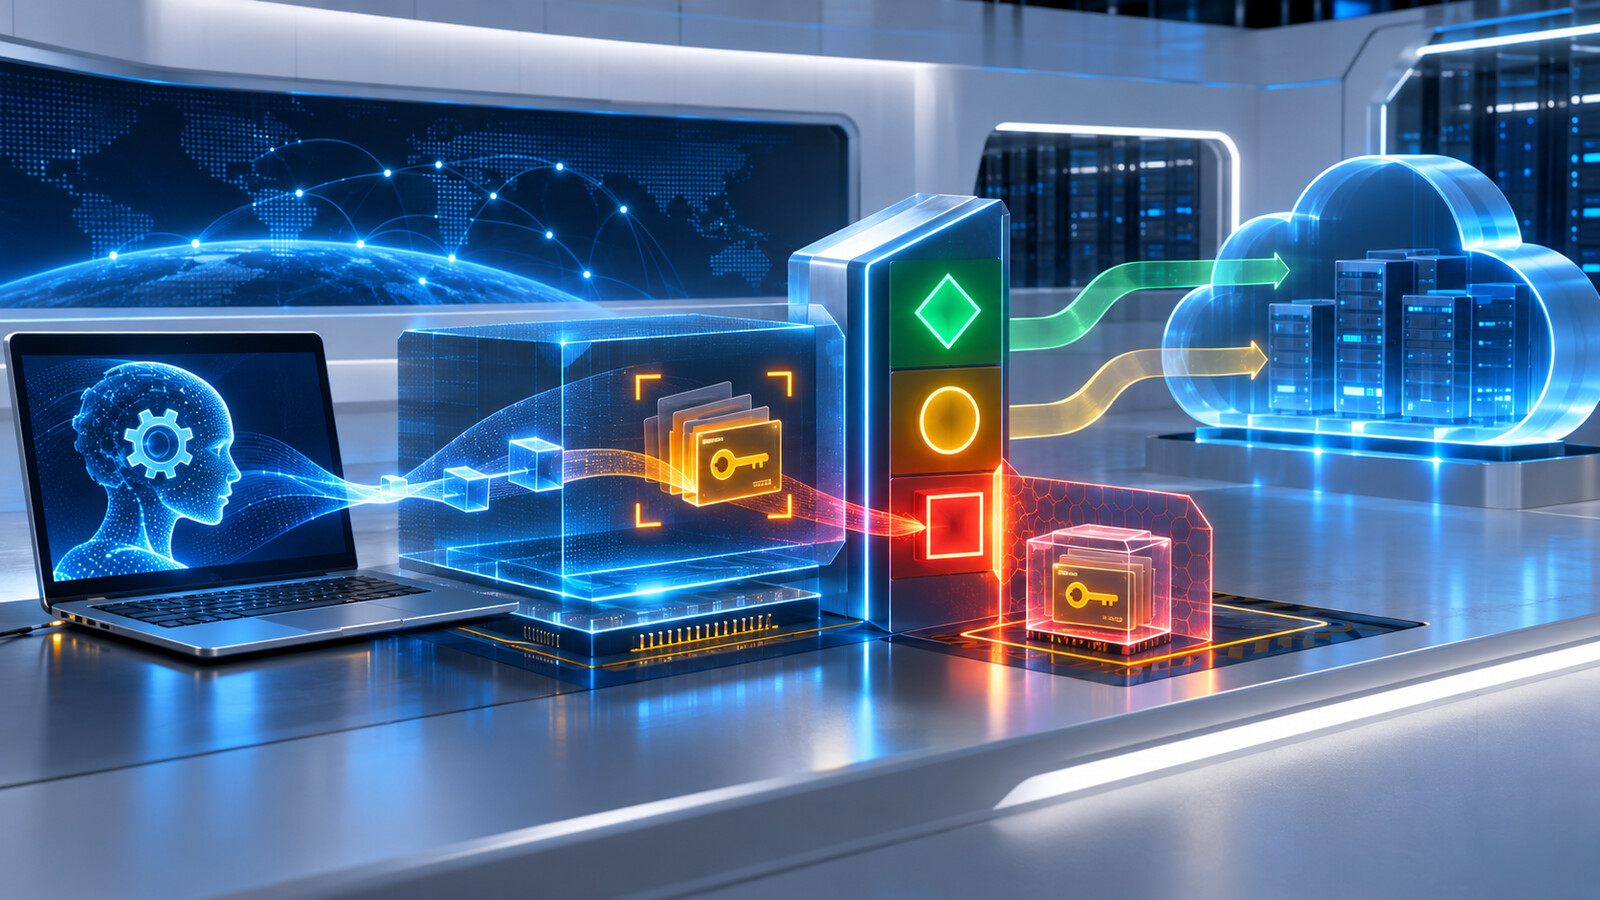
Sysdig made AI Defense generally available on November 4. The product monitors actions AI agents take from a developer workstation to the cloud resources those credentials can reach. According to Sysdig’s product page, the system is designed to stop steps that move beyond defined boundaries before the action completes.
The approach evaluates the agent harness’s stated intent and tool calls together with the operations observed at the kernel layer. Based on organizational policy, a step can be allowed automatically, sent for user confirmation or blocked. Sysdig says it links activity on macOS and Windows workstations with the context of reachable cloud resources.
This model produces a separate execution decision for each action instead of relying only on instructions given to the model. In production, policy errors, agent-framework compatibility and the workflow impact of false blocks should be measured separately.
Explore the original sources
Source date: 4 November 2026.
Published by AI Radar: 4 Nov 2026, 18:13 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…