
Cloudflare links OpenAI Daybreak from code vulnerabilities to edge defense
Cloudflare’s early-access security service uses OpenAI Daybreak models to investigate code vulnerabilities, prioritize them with live traffic signals, and propose patches and WAF rules for human review.
AT A GLANCE
Key points
- Combines code analysis with live traffic and security signals
- Proposes patches and custom WAF rules for review
- Customers retain control over every change
- Cloudflare reports a three-day Codex product rebuild
What is changing?
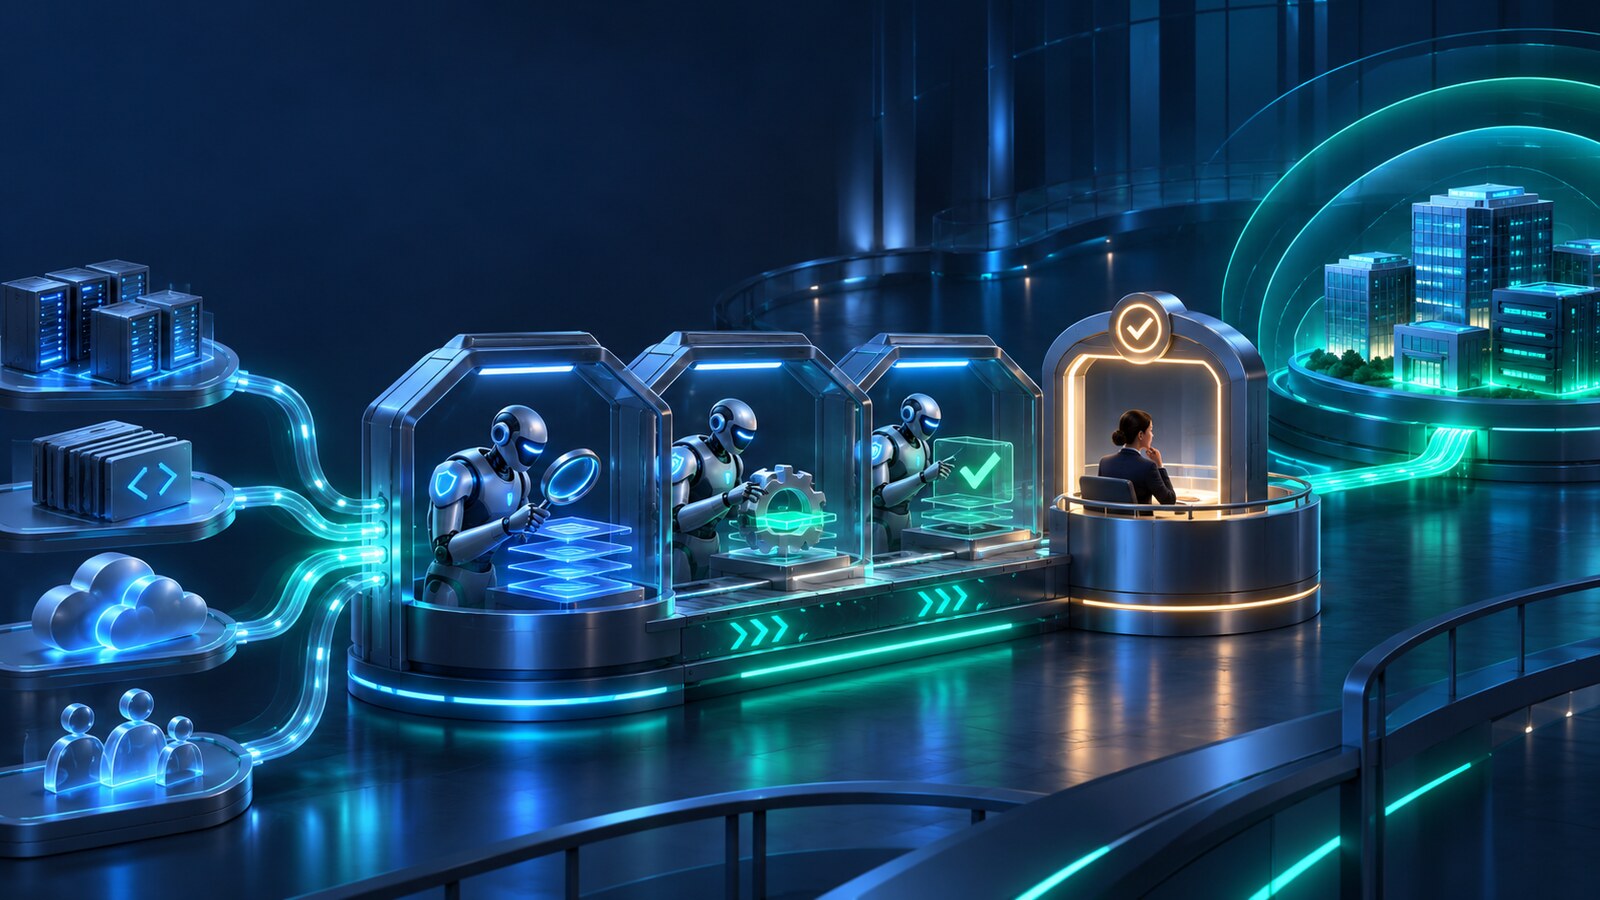
Cloudflare uses OpenAI Daybreak models in its early-access Vulnerability Discovery and Remediation service. The system investigates customer-authorized code for potential vulnerabilities and checks the evidence behind each finding. Cloudflare combines those results with live traffic data, security signals, and existing controls to prioritize routes that are active or exposed to attack.
The service can prepare proposed code patches and custom web application firewall rules to reduce exposure while developers review a permanent fix. Proposals undergo automated checks and Cloudflare team review, while customers retain control over which changes to implement.
According to OpenAI’s customer story, Cloudflare’s network blocks an average of 234 billion threats per day. Cloudflare also says four developers used Codex to rebuild a postponed product in three days with $1,100 in token spend, estimating that the work would otherwise have required roughly ten times more developers.
Explore the original sources
Source date: 21 October 2026.
Published by AI Radar: 22 Oct 2026, 04:09 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.




Loading comments…