OpenAI explains the permission layers behind the Codex command sandbox
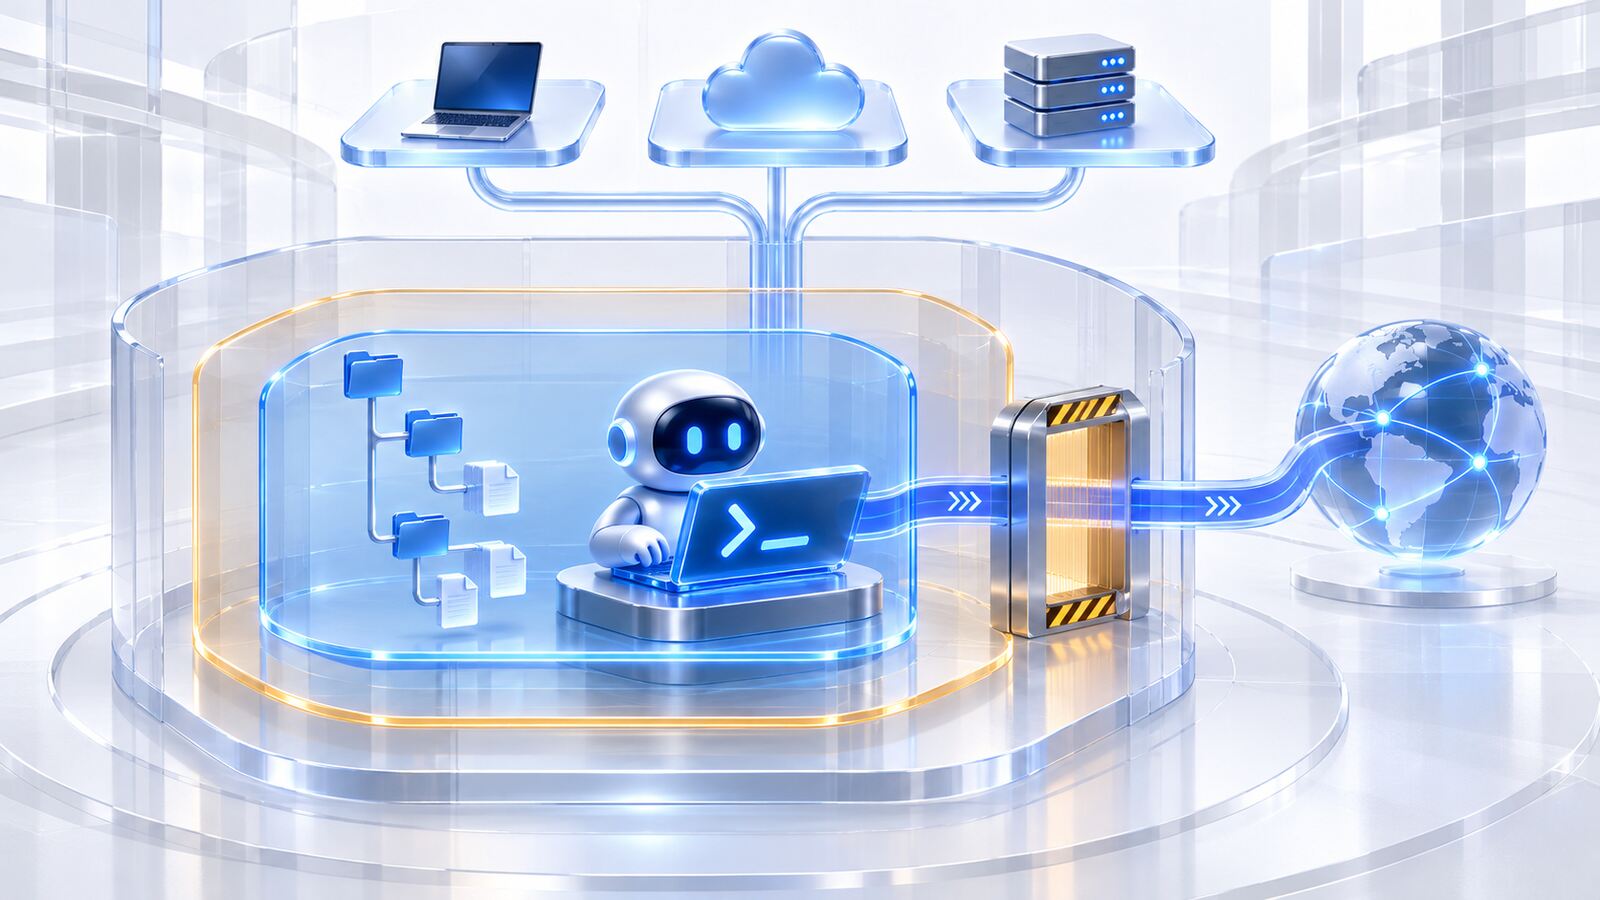
The Codex sandbox runs agent commands in an existing development environment while permission profiles restrict filesystem and network access, using different operating-system mechanisms on macOS, Linux and Windows.
AT A GLANCE
Key points
- Permission profiles can mark filesystem paths as writable, read-only or denied.
- The built-in `:workspace` profile disables networking and keeps `.git` and `.codex` read-only.
- A network proxy enforces domain rules, and descendant processes inherit the sandbox boundaries.
- The `codex sandbox` command makes the same isolation reusable for custom tools and MCP servers.
What is changing?
In an engineering article dated November 18, 2026, OpenAI detailed the sandbox architecture Codex uses when running commands on a computer. Rather than moving work into a separate virtual machine, the approach keeps commands in the user’s existing development environment and constrains access through named permission profiles. Every descendant process inherits the sandbox boundaries of the command that launched it.
The built-in `:workspace` profile permits writes in the workspace while keeping directories such as `.git` and `.codex` read-only. It allows broad reads outside the workspace, subject to existing operating-system permissions, so compilers and SDKs can function; network access is disabled by default. OpenAI explicitly notes that broad reads can expose sensitive material such as API keys in configuration files, while blocking the network also prevents legitimate tasks such as downloading dependencies.
Custom profiles can assign `read`, `write` or `deny` rules to filesystem paths. Network choices include full access, no access, or a proxy that enforces domain rules. Managed requirements let organizations constrain which profiles are available. The `codex sandbox --permission-profile` command exposes the same mechanism outside an agent session; OpenAI demonstrates wrapping an MCP server so it has no network access and can write only to specified directories.
Implementation differs by operating system. Codex uses Seatbelt profiles on macOS, bubblewrap plus seccomp-bpf on Linux, and is transitioning compatible Windows devices to MXC-based isolation. A shared network proxy enforces domain rules, while operating-system restrictions block unauthorized direct connections. OpenAI also stresses that the sandbox does not prevent every harmful behavior; for example, a modified local package could later execute outside the sandbox.
This report is prepared with AI assistance and checked against sources. Automated checks do not constitute human editorial review. Editorial approach
Explore the original sources
Source date: 18 November 2026.
Published by AI Radar: 19 Nov 2026, 09:06 (Istanbul, UTC+3).
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.

Loading comments…