Onyx Security adds runtime governance to Glean agents
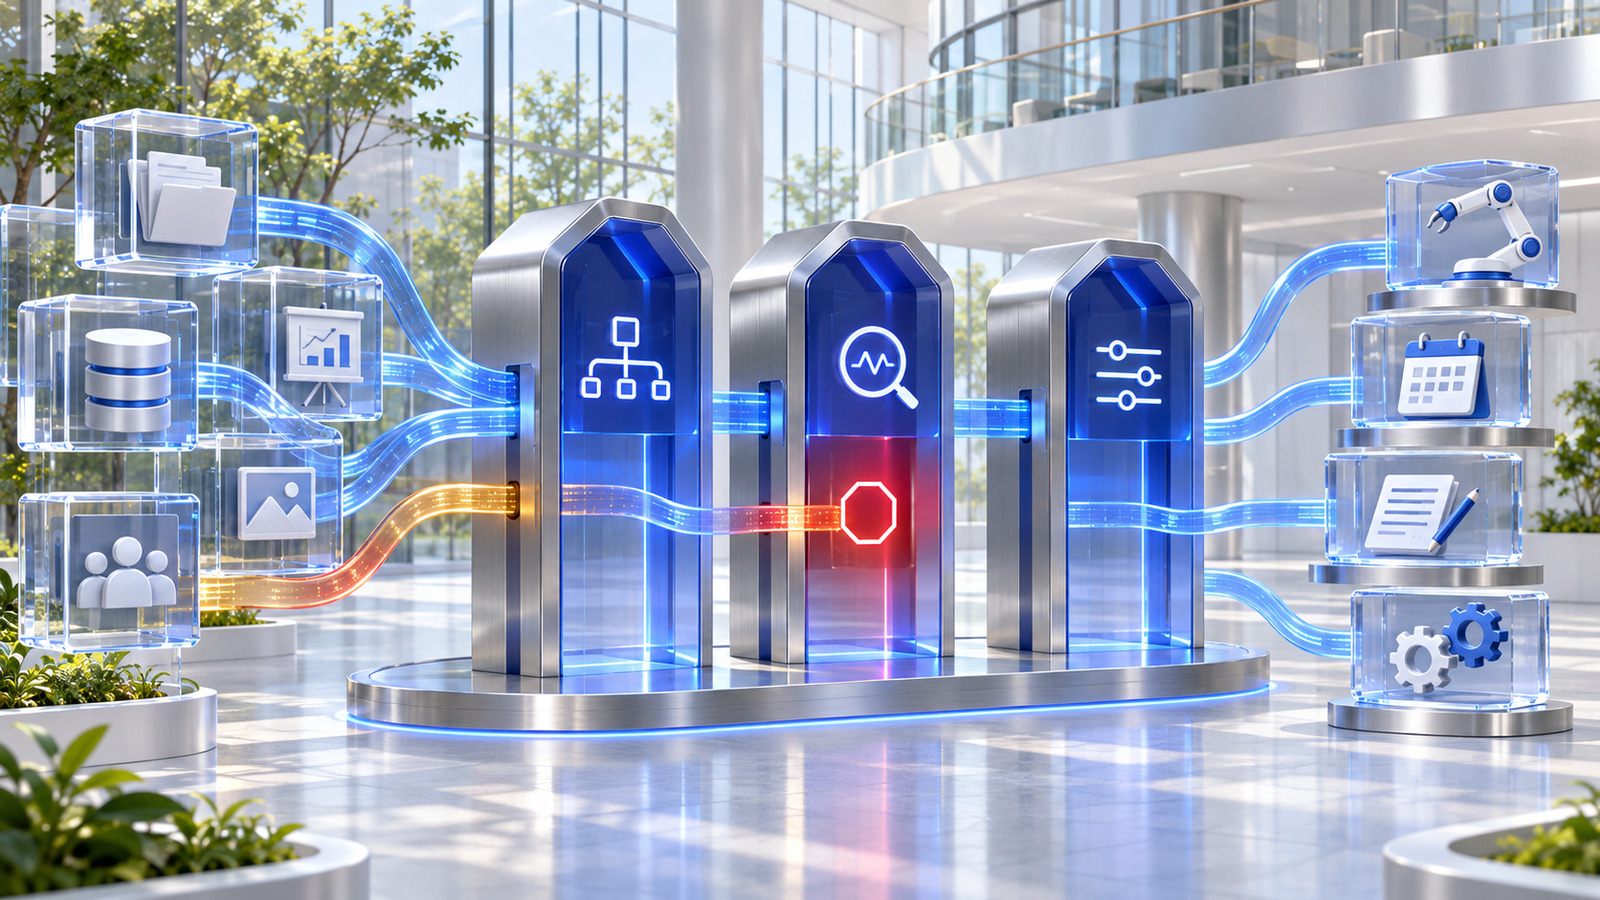
The Onyx Security–Glean integration is designed to expose Glean agent inventory and access posture while evaluating prompts, responses and tool executions against enterprise policy at supported runtime checkpoints.
AT A GLANCE
Key points
- Agent inventory and security posture are discovered through the Glean API in read-only mode.
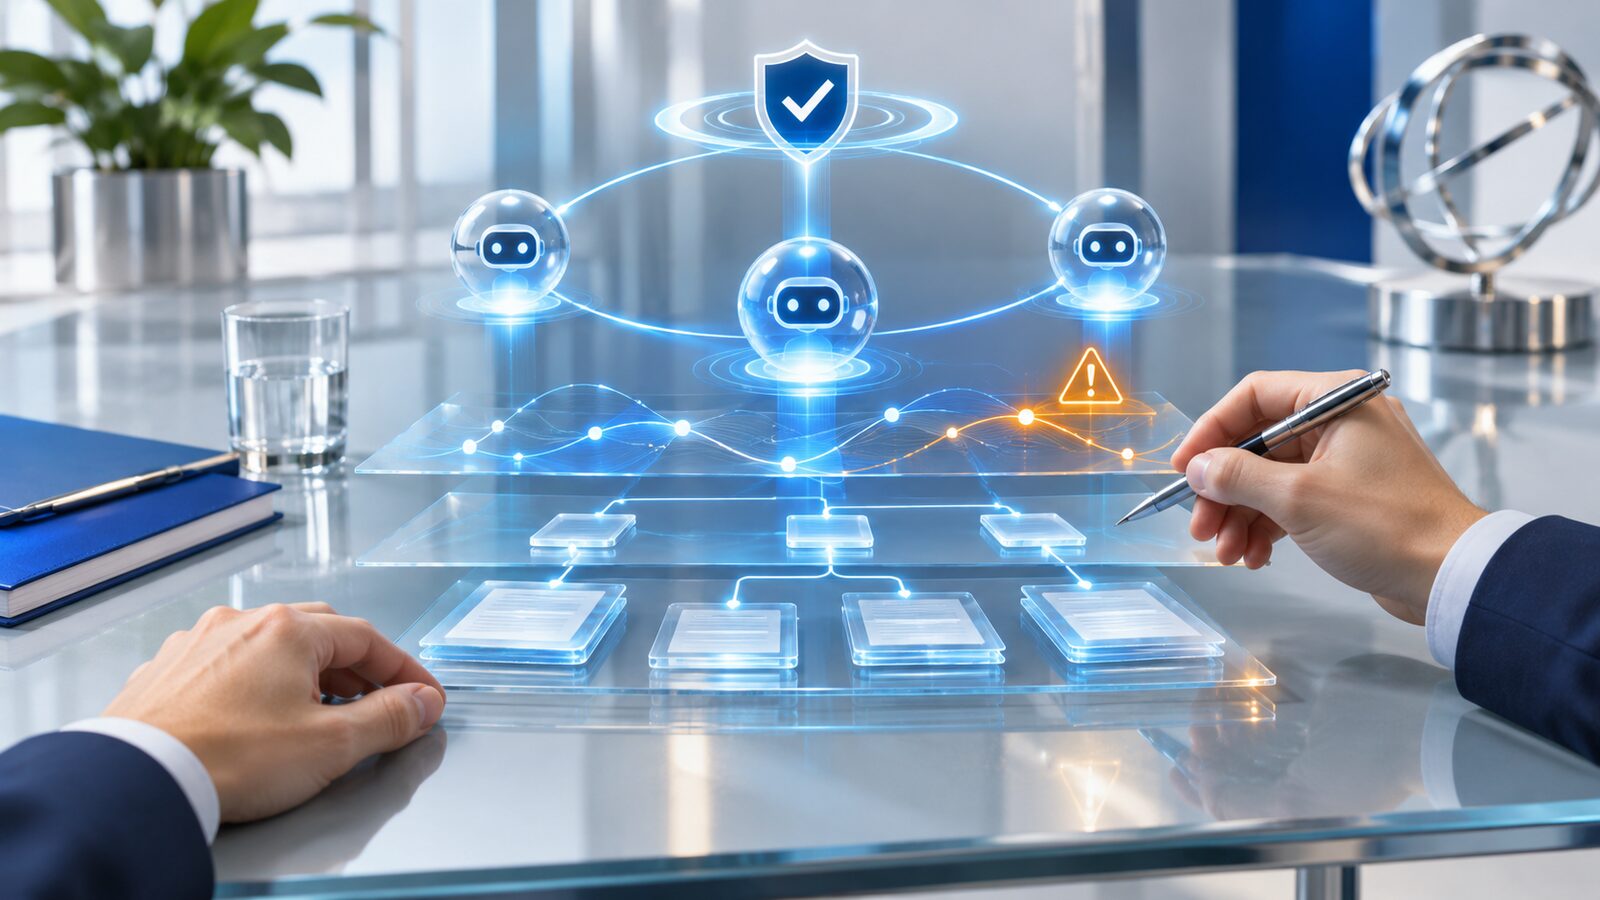
- Prompts, responses and tool executions are checked against policy at supported runtime checkpoints.
- Glean Protect remains the native permissions layer, while Onyx adds enterprise-wide governance and oversight.
- The Onyx connector is listed as beta in the Glean Connector Hub.
What is changing?
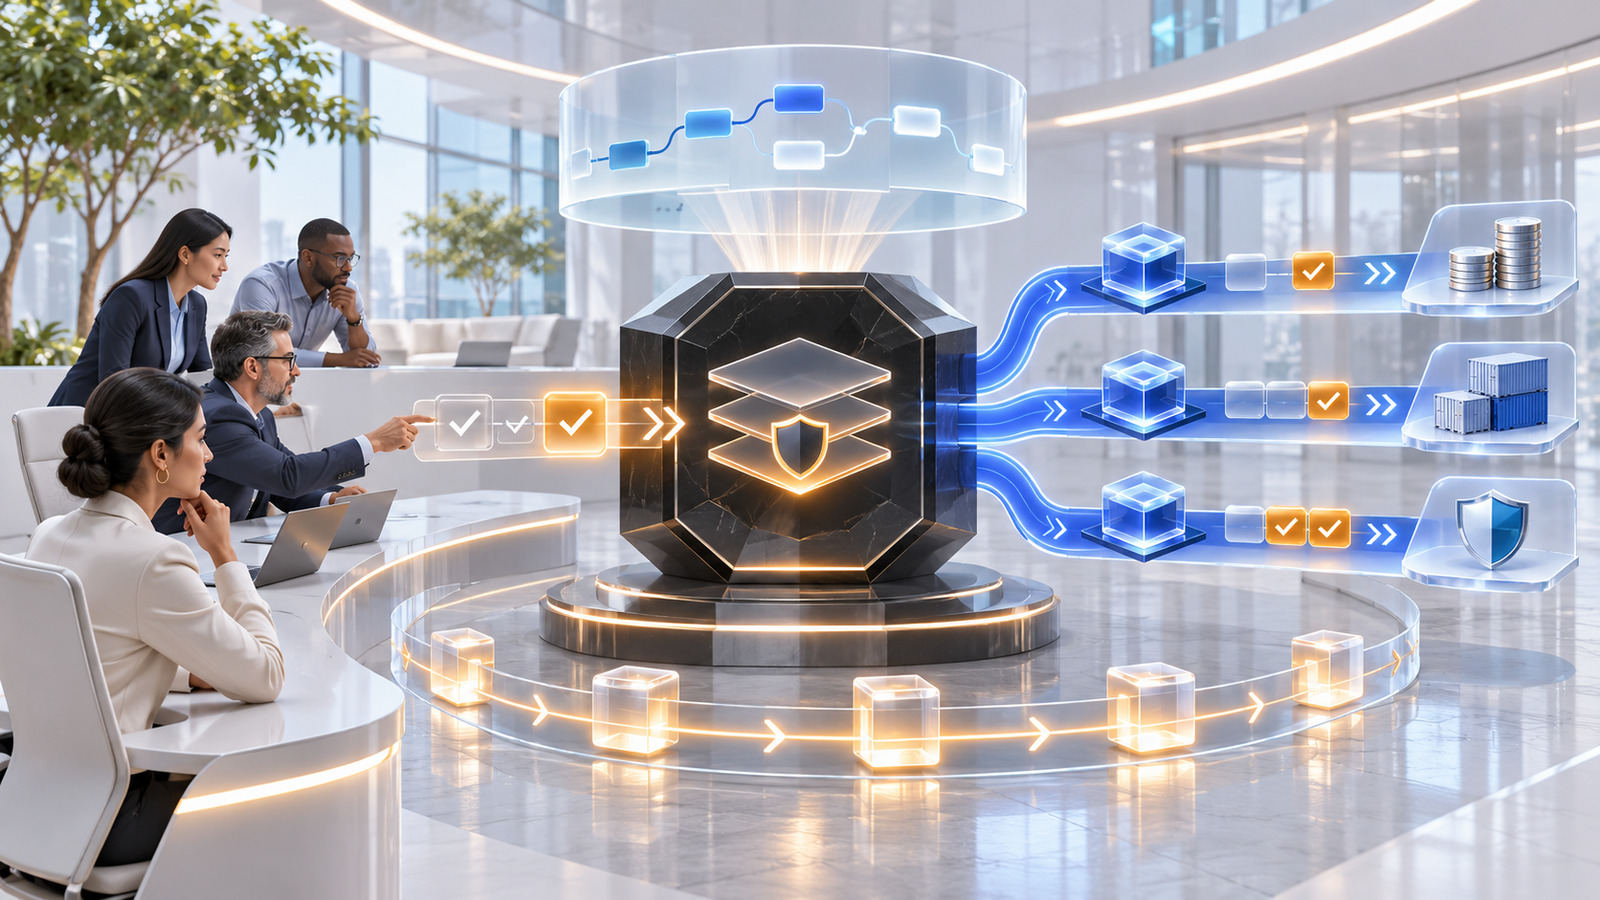
Onyx Security and Glean announced a new integration for enterprise AI agent discovery, risk classification and runtime oversight. Glean supplies permission-aware context connecting agents to enterprise knowledge and business applications, while the Onyx Secure AI Control Plane is intended to track agent ownership, business purpose, access and capabilities in a shared governance layer.
According to Onyx’s technical description, the integration uses the Glean API for read-only discovery of agent inventory and security posture. Glean runtime hooks let Onyx compare conversation content and proposed tool executions with enterprise policy at supported checkpoints. These controls cover blocking unsafe requests, steering actions that depart from user intent, and reassessing changes to permissions, tools or data access.
Glean Protect’s native permissions enforcement, SSO, role-based access, encryption and audit logs remain part of the architecture. Rather than replacing that layer, Onyx adds common inventory, policy and runtime controls across Glean and other supported AI environments. The Onyx connector is listed as beta in the Glean Connector Hub. The announcement provides no independent security test or attack-blocking success rate, so organizations still need to validate supported checkpoints, latency effects and false blocking in their own workflows.
This report is prepared with AI assistance and checked against sources. Automated checks do not constitute human editorial review. Editorial approach
Explore the original sources
Source date: 16 November 2026.
Published by AI Radar: 17 Nov 2026, 06:07 (Istanbul, UTC+3). Updated: 17 Nov 2026, 06:11.
FOLLOW THE TOPIC
Topics and tags
Share your discovery.
Send this story to a friend.
Reader comments
What do you think about this development? Share your experience or question. Comments are published after editorial approval.
Your name/nickname and comment become public if approved. Read: Privacy notice.
Loading comments…